VIDA

Singapore Fintech Festival special: 200 free identity verifications every month with VerifyNow. Limited spots.

Claim Offer

Ryt Bank proves the person, not just the phone, across 3 million devices

Malaysia's first AI-powered bank wanted security its customers would barely notice, and a verified person whenever money or control of the account changes hands. VIDA Auth gives Ryt both: a key locked in each phone for everyday banking, and a live face check matched to the customer's identity wherever the risk is real.

Customer
Ryt Bank
Market
Malaysia · Digital bank
Regulation
BNM RMiT
Customer
Phone Token · Face Token · SPARK

Passwordless for customers. Person-present for fraudsters

Every login and approval at Ryt rides a key locked inside the customer's phone. When the risk goes up, Ryt asks for the customer's live face, and real customers get through

The Result

OTPs, Anywhere
Every login and approval is signed by a key locked in the customer's bound phone. There's no code to intercept or read out.
Zero
high-risk face-auth conversion
Genuine customers pass the face check, so the strongest step doesn't cost Ryt its customers
99%
Authentication success rate
Signatures are verified on Ryt's own servers, so logins keep working even if VIDA is unreachable.
99.9%

THE PROBLEM

Building Malaysia's passwordless bank, with a verified person at the moments that matter

Ryt Bank opened in August 2025 as Malaysia's first AI-powered bank, a venture between YTL and Sea. It set out to run without passwords: customers bind one phone, and that phone approves everything.

A bound phone proves the phone. It doesn't prove who's holding it. So Ryt needed a second kind of proof for the moments fraud actually happens: a new phone, a forgotten passcode, a new payee, a large transfer. And it needed to set out those moments in a way Bank Negara Malaysia's Risk Management in Technology RMiT policy would recognise.

Ryt chose VIDA Auth for both: Phone Token for the everyday, Face Token for the decisive moments, and the SPARK policy engine to decide which one each action needs

3M

device registered

Every one bound to a single customer, with zero OTPs

60s

To move to a new phone

A live face check against the customer's identity, done remotely instead of in a queue

The challenge

Going passwordless removes the obvious attack. It moves fraud to the edges:

  1. Invisible most of the time, decisive when it counts

    Everyday banking had to feel effortless, but adding a payee or moving a large sum needed proof of the person, not just the phone.

  2. Fraud moves to new phones, recovery and coached payments

    Takeover comes in through re-binding and reset paths, and through scams where the customer is talked into approving.

  3. A regulator with a checklist

    RMiT, as reissued in November 2025, asks every bank for one bound device, approvals tied to payee and amount, robust verification before re-binding or recovery, and a kill switch

  4. Always on

    Login can't depend on a vendor being reachable.

The Impact

One platform, one policy, every action covered:

  1. Zero OTPs across 3 million devices

    Every login and approval rides the device-bound key, unlocked by the customer's biometric or passcode

  2. A live face where takeover money moves

    Paying someone new, large transfers, a new phone and changes to account security all ask for the customer's live face. At the highest level there's no code to fall back to.

  3. Security that doesn't cost conversion

    99% of customers pass the face check on high-risk transactions, and 99.9% of authentications succeed.

  4. Evidence for every decision

    Each approval is signed and kept for seven years by a licensed Certificate Authority, ready for an audit or a dispute.

Risk decides when to check. VIDA decides how.

Ryt sorts every action by risk in VIDA's SPARK policy engine. Most of the time the customer barely notices security at all. As the money or the account at stake grows, the check gets stronger, all the way up to the customer's live face

Device

One phone per customer

Each customer binds a single phone, and every login comes from it

Login

No Password

The phone's key signs the login once the customer unlocks it.

Session

Step-up per action

Idle sessions time out. After that, each action gets the check its risk calls for

  1. Level 1 Everyday

    Silent

    Small payments to people the customer pays often

    One tap on the bound phoneProof of device

  2. Level 2 Elevated

    One Touch

    Larger everyday payments

    Tap + fingerprint or face unlockProof of presence

  3. Level 3 High

    Live face

    Raising a limit, a first payment to a saved payee, locking the account or changing its details

    Live face, matched to the customer's identityProof of Person

  4. Level 4 Highest

    Live face, no fallback

    Paying someone new, large transfers, a new phone, and changes to account security.

    Live face, with no code to fall back toProof of Person

Critical Risk

Strong fraud signals, such as a blocklisted device or behaviour that matches an active fraud campaign, stop the action or hand it to Ryt's team

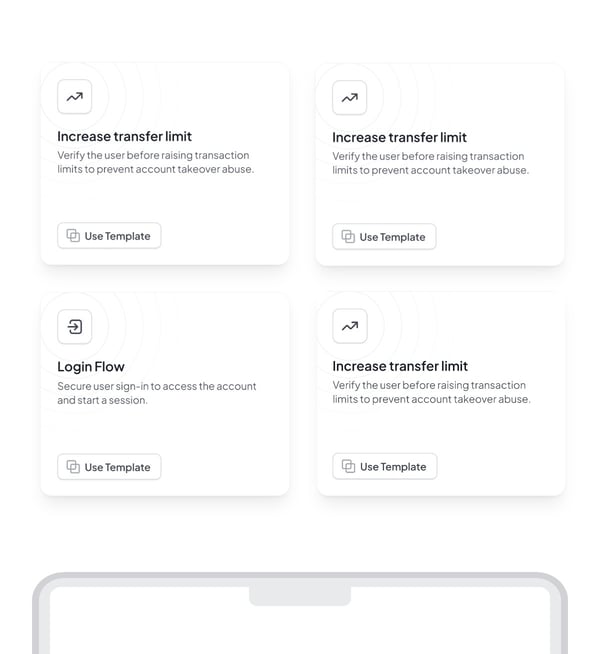
Ready-made policy templates in the SPARK dashboard: increase transfer limit and login flow

Configured in a dashboard, not a release train.

  • Ryt starts from a policy for each action, such as login, a new payee, a limit change or a new phone.
  • For each step, Ryt picks the factor and tunes it: attempts, expiry and device rules.
  • Ryt decides where a fallback is allowed and where there's none.
  • Thresholds and factors change in SPARK, with no app release.
  • Routine login

    Silent device check

  • Larger payment

    Touch to approve

  • New payee + large amount

    Live face, no fallback

  • Critical fraud signal

    Blocked or reviewed

How it work

The right phone, the right person, this payment.

What happens when a Ryt customer sends a large payment to someone new

Step 1

SPARK reads the action

SPARK reads the action.

A new payee and a large amount put the payment at the highest risk level.
How Ryt's setup lines up with BNM's RMiT

Ryt sorts every action by risk in VIDA's SPARK policy engine. Most of the time the customer barely notices security at all. As the money or the account at stake grows, the check gets stronger, all the way up to the customer's live face

01

In Production

One bound device per customer

where is it : App 3 · 3(a)–(b) · 10.22

Each customer binds one phone. The key is created in the phone's hardware keystore and can't be copied, synced or restored onto another device

02

In Production

Approval tied to payee and amount

where is it : App 3 · 6(a)–(f)

Phone Token signs the exact amount and payee on the phone. Change anything and the signature breaks

03

In Production

Robust verification for a new phone or number

where is it : App 3 · 1(a) · 3(c)–(e)

Binding a new phone or changing the mobile number needs the customer's live face, matched to their identity.

04

In Production

Kill switch and validated restoration

where is it : 12.8(a)–(c) · App 3 · 3(d)

Customers can lock their account from the bound phone.Getting back in needs a live face matched to their identity, and Ryt's team steps in where the policy calls for it.

05

In Production

Don't rely on phone biometrics alone for payments

where is it : App 11 · 2(f)

At the high-risk levels, Ryt asks for a face matched on its side against the customer's identity, not the face or finger saved on the phone

06

In Production

Detect AI-driven takeover

where is it : App 3 · 1(a) · 3(c)–(e)

Every face check runs certified liveness against deepfakes, masks and screen replays PAD Level 3

07

In Production

Interrupt coached and hijacked payments

where is it : App 11 · 3 · 5

Paying someone new and large transfers need a live face with no fallback. There's no code for a scammer to ask for.

08

In Production

MFA for financial and high-risk non-financial actions

where is it : App 3 · 4(a)–(c)

Medium- and high-risk actions, such as adding a payee or raising a limit, need two factors. Device, person and payment are recorded as one signed event.

09

In Production

A password-free login option

where is it : App 3 · 1(a) · 3(c)–(e)

Zero OTPs and no password to phish or reset: every login is signed by the bound phone's key

Cloud and outsourcing  RMiT Appendix 10  VIDA's platform was assessed under RMiT Appendix 10 and cleared for the Ryt Bank deployment.
RMiT obligations sit with the bank; VIDA supplies the controls and the evidence.

One platform for person present authentication

The same components Ryt runs in production,
available to any bank or e-wallet.
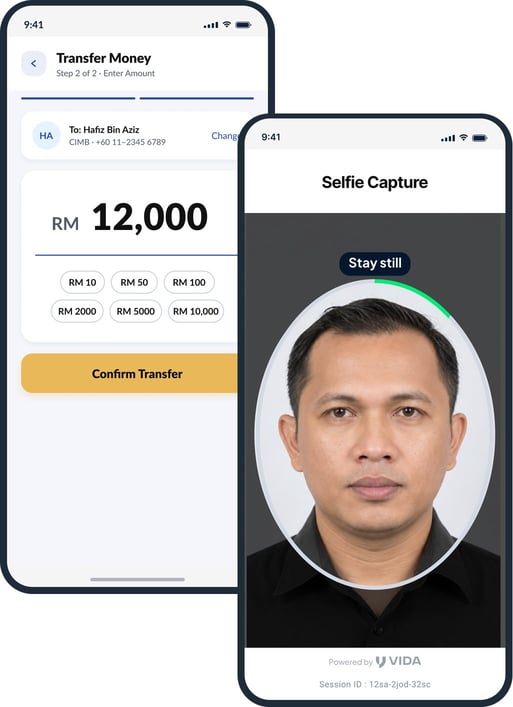
Ryt app screens: a transfer of RM 12,000 and the selfie capture that approves it

Phone Token

A key locked inside the phone. It approves logins and payments in under 50 ms P95, and keeps re-checking the phone it lives on

Face Token

A live face, matched on the bank's side against the customer's identity. Certified against deepfakes, masks and screen replays PAD Level 3

SPARK policy engine

Set the proof each action needs, with thresholds and fallbacks, from a dashboard. No app release.

Signed audit trail

Every approval is signed and kept for seven years by a licensed Certificate Authority, with dashboards and maker-checker for ops

What VIDA delivers for leading businesses

  • Telkomsel
  • Indosat Ooredoo Hutchison
  • XLSMART
  • yes
  • Ryt Bank
  • BCA
  • BRI
  • Grab
  • ByteDance
  • GoTo

Discover the Industries

P2P Lending

Stay ahead of deepfake risks in P2P lending with enterprise-grade, real-time verification.

Banking & Digital Banking

Protect institution from AI-driven fraud and safeguard customer trust with reliable identity solutions.

Multifinance

Ensure secure multifinance applications with fast, compliant solutions.

Consumer Lending

Secure every step of the journey with fast, accurate identity verification.

Buy Now Pay Later

Safeguard transactions with fast, real-time verification to ensure trust and compliance.

Healthcare

Protect healthcare access with the right digital identity solutions.

Let’s make your first auth flow today.

Pick one journey. In 4-6 weeks, you’ll have proof against criteria you set. New-phone enrolment is a good place to start.
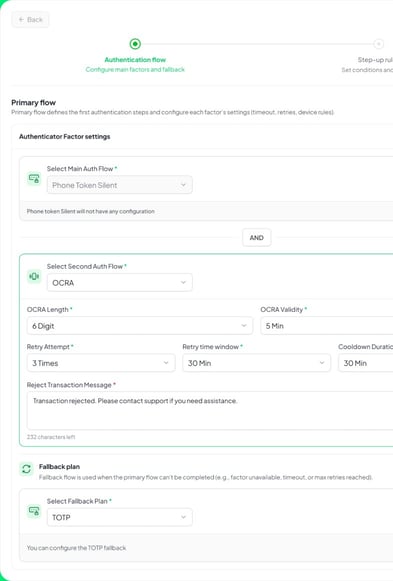
VIDA authentication flow settings: primary flow, second factor and fallback plan

WHAT TO EXPECT

01

Working session

Half a day with your digital, risk and fraud leads, mapping your journeys to the ladder.

02

Proof of concept

One flow, 4–6 weeks, with pass/fail criteria agreed upfront.

03

Rollout

Users switch silently, alongside your current tokens. Then step up by risk.

Fraud doesn’t wait. Neither should you.

Safeguard every customer, every transaction, every time. Talk to VIDA today.
Green padlock with a fingerprint