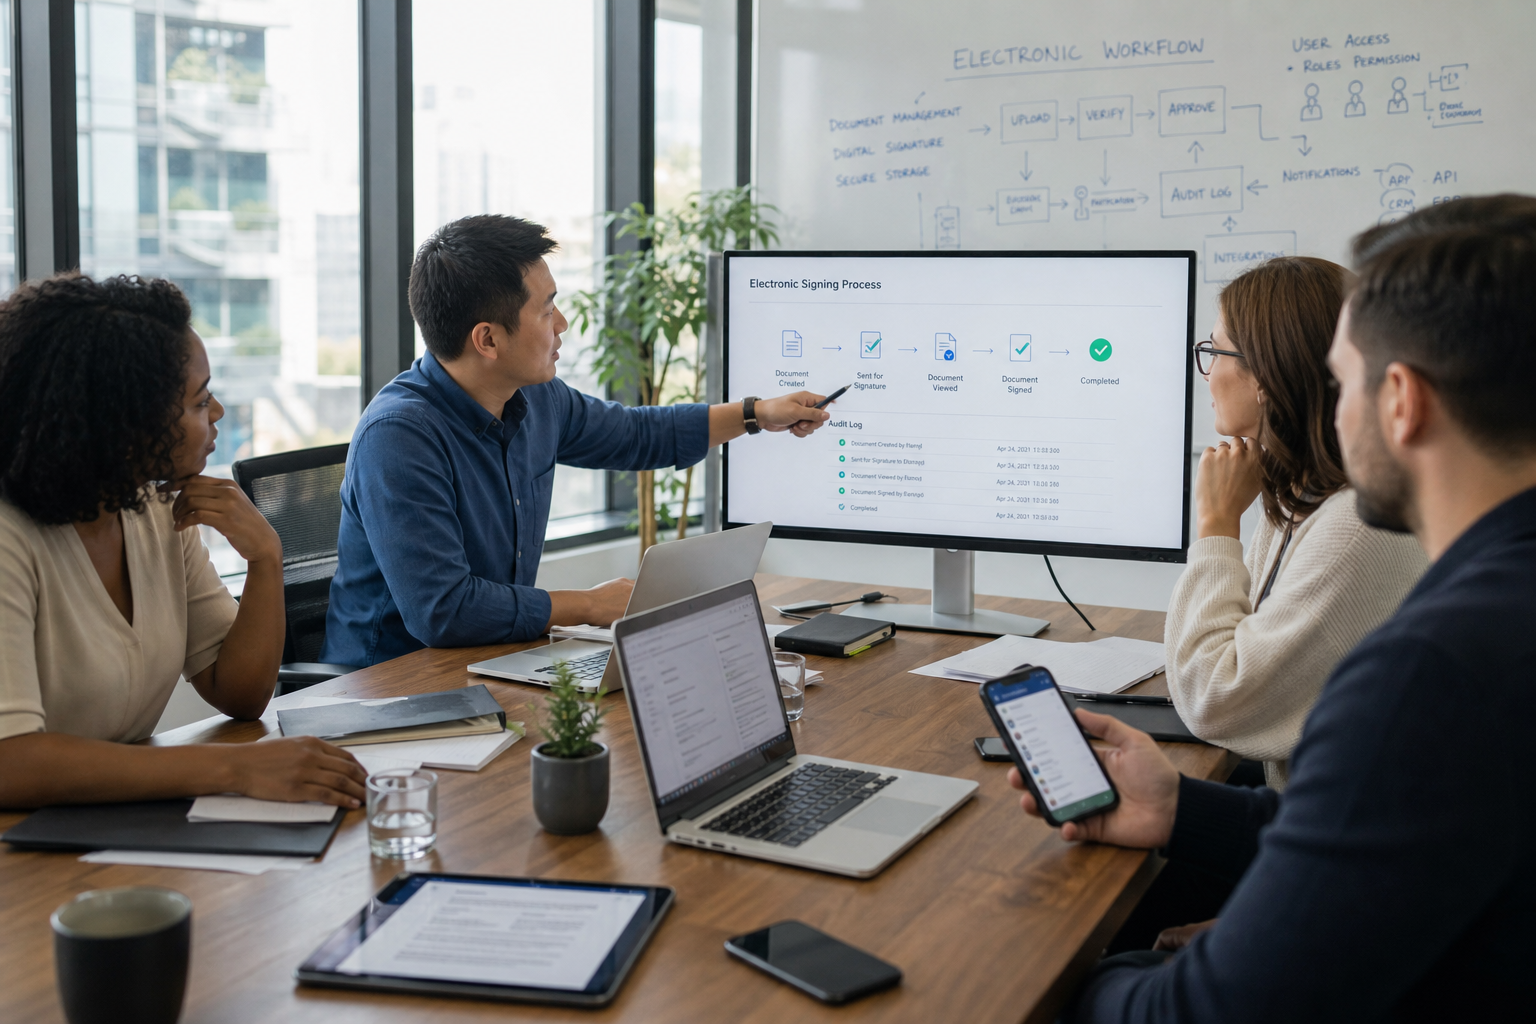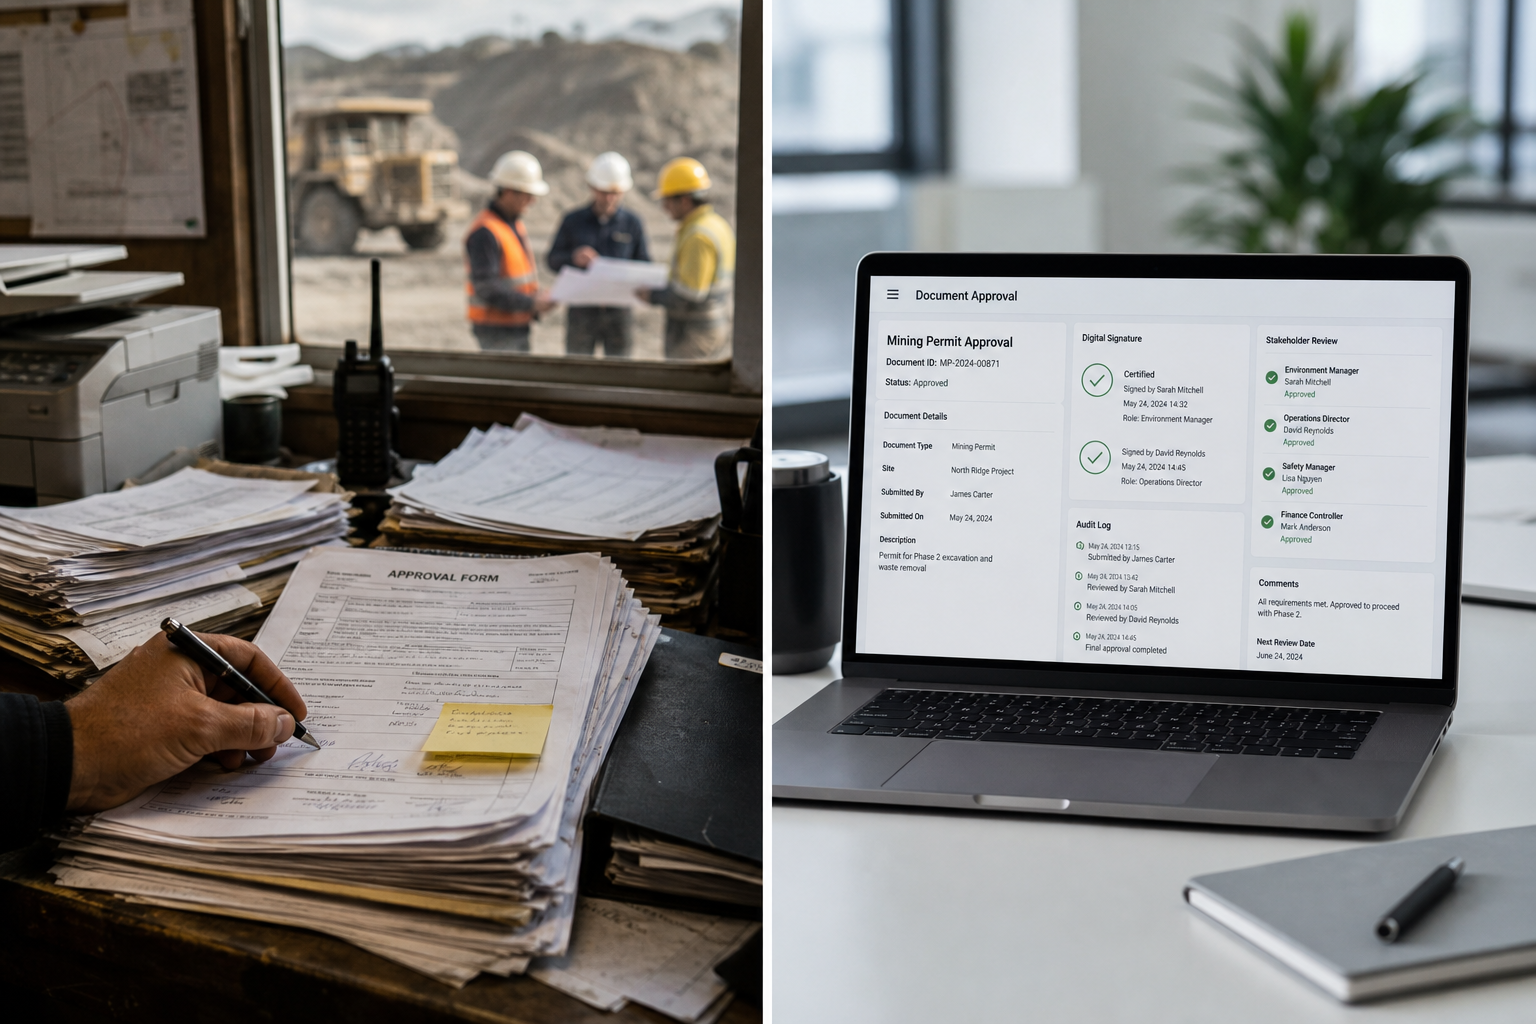
Electronic signatures are already part of how businesses in Malaysia handle documents. Yet digital signing does not always happen through a dedicated e-signature platform. Many businesses still use PDF fill-and-sign tools or messaging apps as part of their approval and signing workflows.
This raises an important question: when is an electronic signature considered reliable enough for a business transaction?
In Malaysia, the Electronic Commerce Act 2006 (ECA 2006) provides the legal framework for electronic signatures in commercial transactions. Section 9 outlines key requirements that help establish whether an electronic signature can be relied upon.
Understanding these requirements can help businesses build signing workflows with clearer verification and stronger evidence.
Read More: e-Sign is Now Available in Malaysia
What Section 9 of the ECA 2006 Says About Electronic Signatures
Section 9 of the ECA 2006 sets out requirements for an electronic signature used to authenticate an electronic message or document.
In practice, the signature needs to do three things. It should identify the person signing, be associated with the document, and be created using a method that is reliable for its intended purpose.
These requirements matter because an electronic signature is not simply about placing a name, image, or mark onto a document. The signing process should also provide a way to establish who signed and connect that action to the document being signed.
For businesses, this means the signing method and the evidence surrounding the transaction are both important parts of a digital signing workflow.
The Three Things an Electronic Signature Needs to Show
1. The signer can be identified
A signing process should provide a way to establish who performed the signing action.
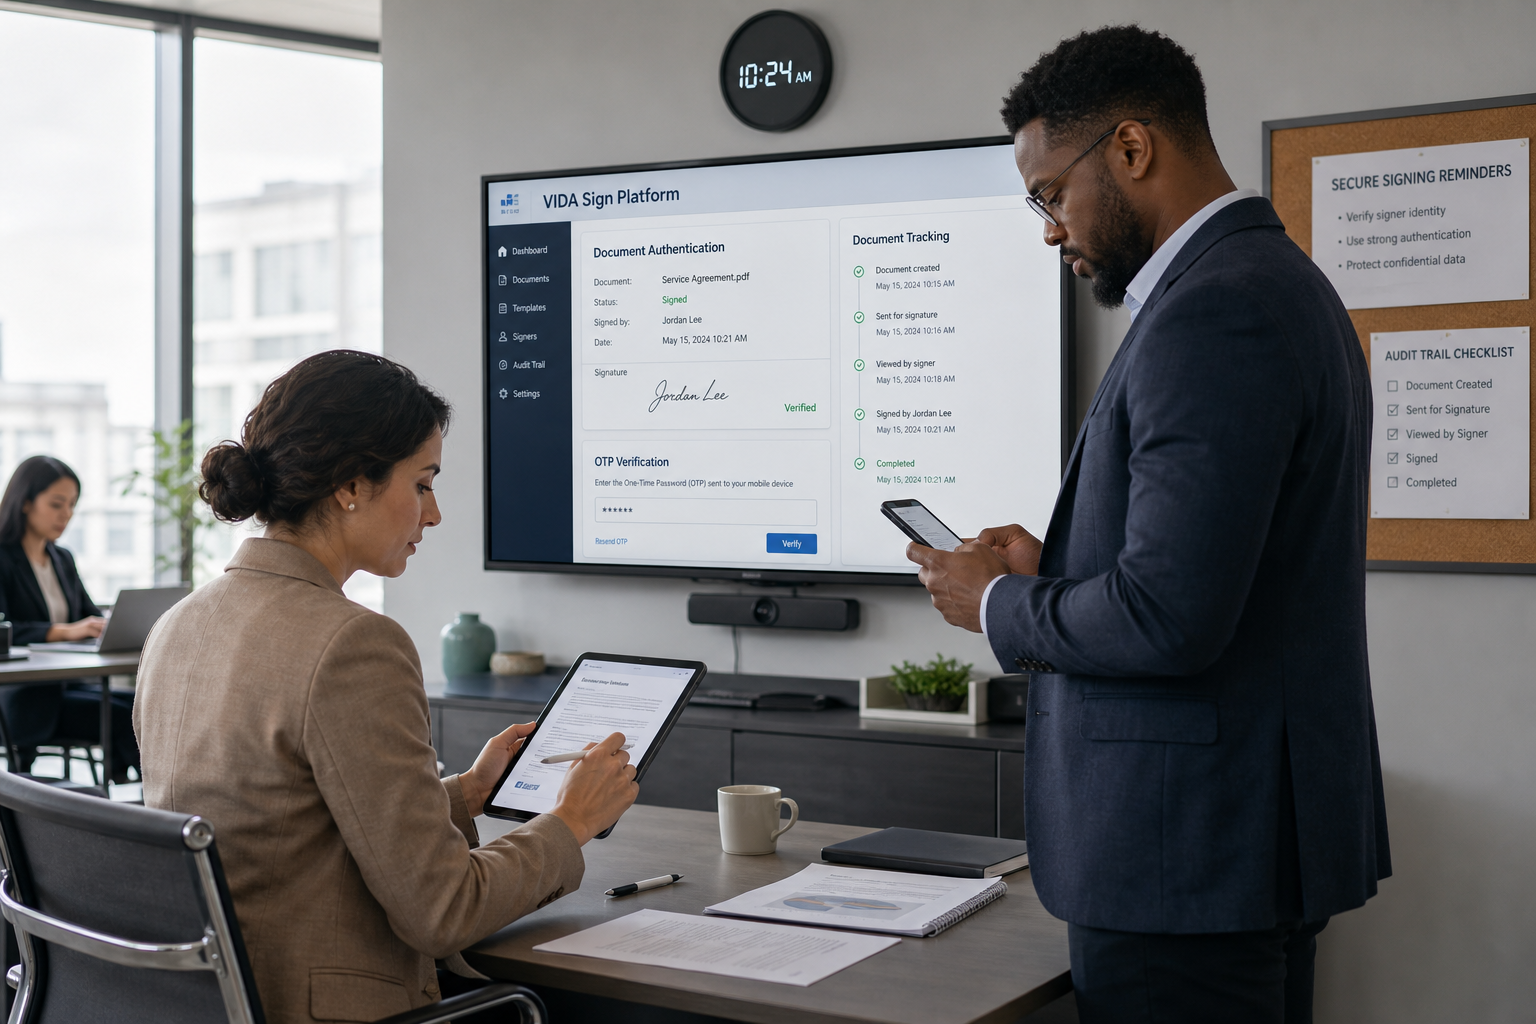
This is where authentication becomes important. For example, email OTP adds a verification step by requiring the signer to enter a one-time code sent to their registered email address.
The OTP creates a verifiable, time-stamped action connected to the signer and the signing process, rather than relying solely on a signature mark placed on a document.
2. The signature is associated with the document
The signing action should be connected to the specific document being signed.
This becomes particularly important when documents move through multiple people, revisions, or approval stages. A structured signing process can keep the signature and the document together, making it easier to establish what was actually signed.
Document tracking and signing records therefore play an important role alongside the signature itself.
3. The signing method is reliable
The method used to create the signature should be reliable and appropriate for its intended purpose.
Reliability is not only about the act of signing. It also involves the surrounding process that verifies the signer and records what happened during the transaction.
This is where features such as authentication, document tracking, and tamper-proof records become relevant. Together, they provide a more structured record of the signing process.
Why Email OTP and Audit Trails Matter
Email OTP and audit trails address different parts of the signing journey.
Email OTP helps verify the person performing the signing action. Once the OTP is successfully entered, the transaction has an additional authentication event tied to the registered email address.
An audit trail, meanwhile, records the activities surrounding the signing process. It can provide evidence of what happened throughout the transaction, helping businesses keep track of document activity and signing status.
This distinction is important because a signature by itself does not tell the complete story. Businesses may also need to understand who signed, what document was signed, and how the signing process took place.
A structured electronic signing platform brings these elements together, creating a clearer record from the moment a document is sent through to completion.
Moving Beyond Scattered Digital Signing Workflows
Digital signing does not always happen in one dedicated environment.
It is common for businesses to rely on a mix of tools depending on the document and situation. PDF fill-and-sign is often used to complete documents, while messaging apps serve as a channel for approvals and document exchanges. Dedicated e-signature platforms are part of this mix, but not necessarily the default for every signing workflow.
The challenge is not simply whether a document can be signed digitally. It is whether the business has a consistent way to authenticate signers, track documents, and retain evidence of the signing process.
For businesses handling contracts, HR documents, purchase orders, approvals, and other agreements, bringing these steps into a structured signing workflow can make the process easier to manage.
Meet VIDA Sign
VIDA is a digital identity and electronic signing platform designed to help businesses manage trusted digital transactions.
For the Malaysia market, VIDA Sign Platform (VSP) provides a no-code, ready-to-use electronic signing experience. Businesses can upload documents, add signers, and manage the signing process without technical integration.
The platform is designed to adapt the signing experience to the user's region. For Malaysian users, email OTP is included as part of the signing flow, while document activity is tracked through an audit trail and completed documents are protected with tamper-proof signing records.
This gives businesses a more structured way to manage electronic contracts and other documents that require signatures, from sending and authentication through to completion and tracking.
Read More: Fraud Doesn’t Care About Company Size, It Looks for Security Gaps
As digital signing becomes part of everyday business workflows, the focus is no longer only on replacing wet-ink signatures. It is also about creating a signing process that can clearly establish the signer, connect the signing action to the right document, and provide reliable evidence of what happened.
For businesses, understanding these requirements is a practical first step toward building a more trusted electronic signing workflow.